Corrlinks Leaks Explained: Everything You Need to Know About Inmate Email Privacy
 By James H. Sterling
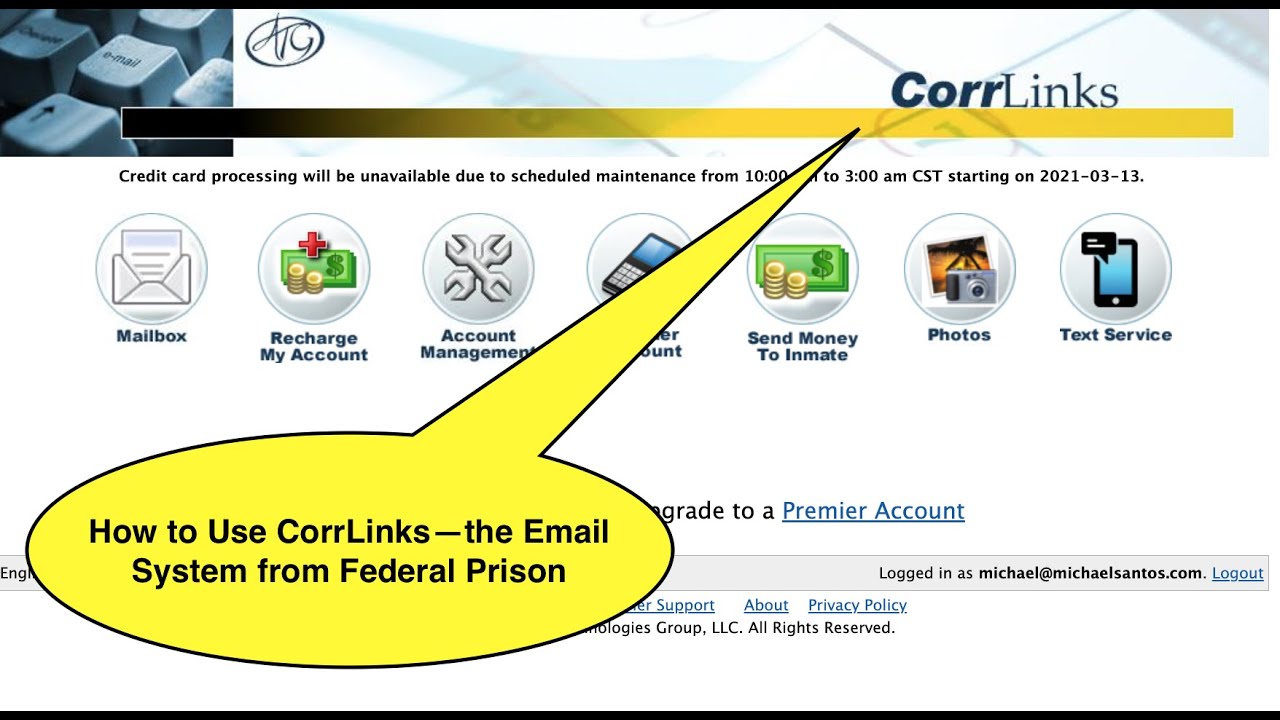
To understand where the security vulnerabilities lie, one must understand how prison email actually functions. CorrLinks is not a standard email provider. It is the public-facing portal of the Trust Fund Limited Inmate Computer System (TRULINCS), a closed communications network operated within the Federal Bureau of Prisons (BOP) and managed by Advanced Technologies Group (ATG), a private contractor subsidiary of TKC Holdings.
When an incarcerated person sits down at a shared terminal, their outgoing messages never travel across the open internet. The text remains inside the ATG infrastructure. Outside contacts must log into the web portal or mobile application to read and reply to those dispatches.
This architecture allows the system to enforce strict surveillance protocols:
- Messages are capped at 13,000 characters and cannot contain attachments, embedded photos, hyperlinks, or active code.
- The system subjects every outgoing and incoming communication to automated keyword screening, flagging terms related to contraband, institutional security, or criminal conduct.
- Flagged messages drop into an administrative queue for human review by correctional intelligence officers, delaying delivery from twenty minutes to several days.
- All data is preserved in accessible state and federal law enforcement databases for years, accessible to prosecutors upon request without a search warrant.
Because ATG centralizes millions of sensitive familial records across federal facilities and multiple state departments of corrections, it represents a high-value target for threat actors interested in identity theft, extortion, and intelligence gathering.
James Sterling reports on renewable energy developments, climate policy, ecological conservation, and green tech innovations around the globe.
