Official Netflix Qr Code vs Phishing Fake: Visual Clues to Protect Your Credentials
 By Sophia Al-Mansoor
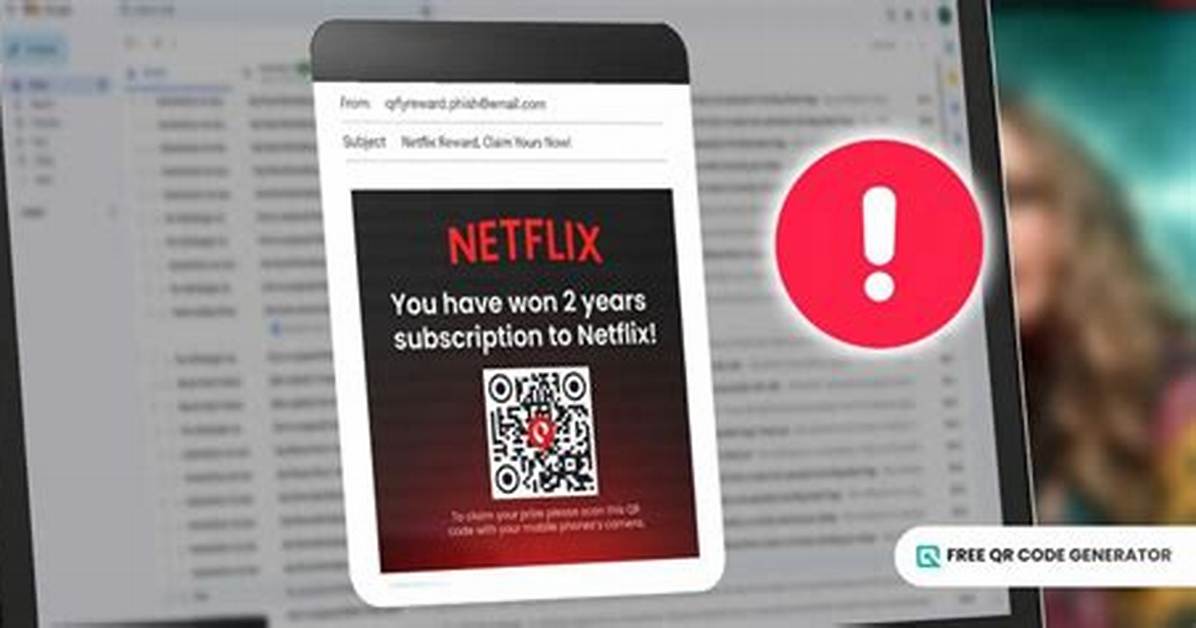
Users often fall victim not through technical illiteracy, but because of how consumer mobile devices parse encoded information.
Default camera applications on modern iOS and Android versions show a brief preview of the destination URL before opening it. However, threat actors bypass visual inspection using dynamic shorteners and open redirect exploits. A scanned code might initially display an unalarming domain, only to cascade through multiple HTTP 302 redirects before dumping the user on a deceptive harvesting form.
Third-party scanner apps pose even steeper security hazards. Ad-supported QR code readers downloaded from marketplace storefronts frequently lack URL preview functions altogether. Worse, security teams have identified dozens of malicious QR scanner apps in app store ecosystems that quietly inject tracking parameters or hijack browser sessions directly, complicating phishing URL detection.
NordVPN documented in early 2026 that streaming-related quishing attacks now routinely deploy reverse-proxy infrastructure such as Modlishka or Evilginx. In these attacks, the scammer's server sits directly between the victim and the actual Netflix server. When the victim enters their credentials and temporary two-factor authentication tokens, the proxy captures both, completing an automated account takeover before the user realizes their session was intercepted.
Sophia analyzes international trade, startup ecosystems, retail transformation, and supply chain logistics for modern digital publications.
