Legit or Phishing Trap? Visual Proof Behind the Viral Youtube Verification Text Phenomenon
 By James H. Sterling
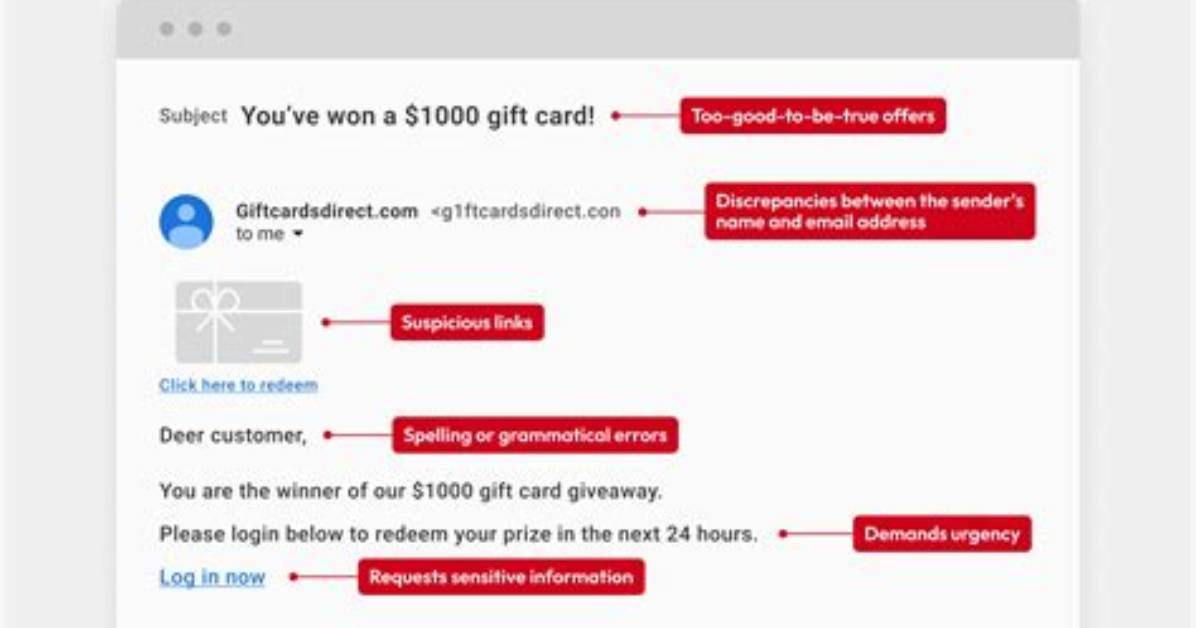
Understanding the technical boundaries between actual Google authentication infrastructure and external phishing campaigns prevents account loss. Google's actual security framework generates and evaluates time-based and cryptographically signed tokens on centralized authentication servers. Users never compute cryptographic hashes or verification values manually.
| Security Parameter | Official Google Verification | Fraudulent "Calculation" Lure |
|---|---|---|
| Originating Message | Verified carrier shortcode (e.g., 22000 in North America) containing pure numeric codes. | Unregistered 10-digit mobile numbers, VoIP lines, or spoofed international numbers. |
| Interactive Action Required | Entering a displayed 6-digit code or tapping an on-device prompt inside an existing session. | Clicking an embedded hyperlink to access an external tool to "calculate" or "sync" credentials. |
| Delivery URL Domain | Direct top-level domains: accounts.google.com or myaccount.google.com. | Obfuscated redirects, free subdomains, or misspelled spoof domains (e.g., accounts-security-yt[.]com). |
| Authentication Method | Cryptographically signed TOTP tokens, hardware FIDO2 keys, or system-level Google Prompts. | Adversary-in-the-Middle (AiTM) reverse proxy capturing entered text strings in real time. |
| Immediate Outcome | Seamless user access to YouTube Studio without profile modification warnings. | Session cookie theft, primary email detachment, channel rebranding, and immediate lockout. |
James Sterling reports on renewable energy developments, climate policy, ecological conservation, and green tech innovations around the globe.
Tags:
here to calculate verification codes in text youtube
